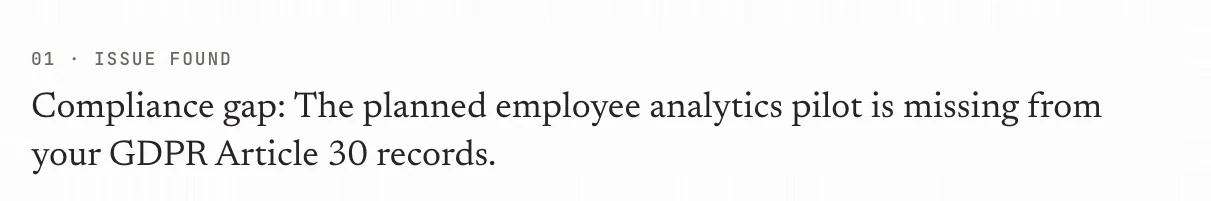Compliance should start with what matters for the company stage.
Cut through regulatory complexity. Know exactly what applies to your company stage and skip what doesn't. Practical compliance for founders, not lawyers.
Checklist
Minimum viable compliance first. Then the system.
The hub keeps FAQs and resources tied to first compliance actions.
01
Privacy policy published
02
Cookie banner implemented
03
DPAs with vendors signed
04
Processing register created
05
Data subject rights process
06
AI risk classification (if applicable)
07
DPIA for high-risk processing (guided wizard in Lexi)
What changed, and why
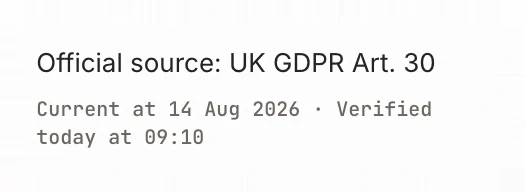
An official source becomes a compliance gap you can act on.